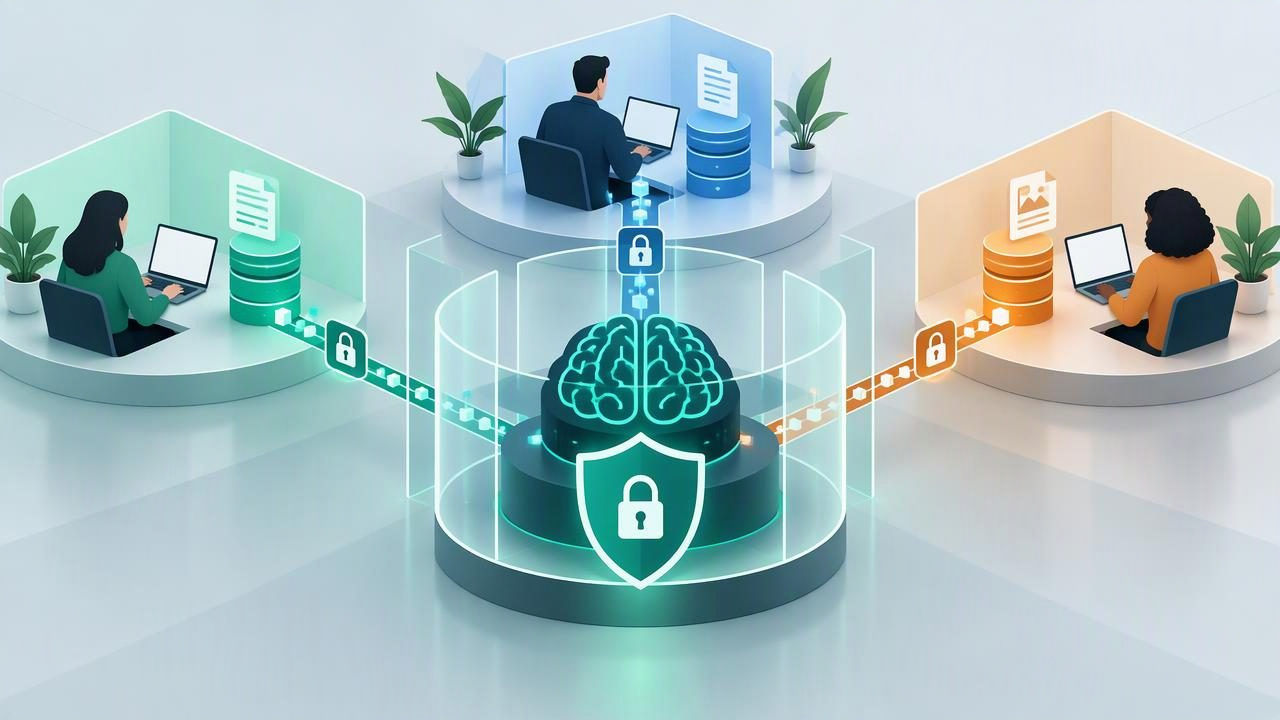
When an agency manages AI agents for several businesses, one client’s conversations, files, or settings must never appear in another client’s workspace. Knowing how to separate client data safely is therefore a core part of building trustworthy multi-client operations—not an optional technical detail.
This guide explains the controls that help protect client information across AI agents, WhatsApp conversations, knowledge bases, team access, and operational records. Whether you use a managed AI agent cloud or self-hosted software, the goal is the same: make each client’s data accessible only to the people and processes that are authorized to use it.
Why client data separation matters
Agencies often handle information that should remain private: customer phone numbers, support histories, sales inquiries, uploaded PDFs, internal instructions, and business-specific pricing. If an agent retrieves the wrong client’s document or a team member opens the wrong inbox, the result can be a privacy incident, lost trust, and potential legal or contractual consequences.
AI adds extra pathways for accidental exposure. A model may receive retrieved text as context, while an application may store messages, embeddings, tool results, and handoff notes in different systems. Protecting data means securing every pathway—not just separating the visible client dashboards.
Start with a clear tenant boundary
A tenant is the isolated environment assigned to a client. Define what belongs inside it before configuring agents. At a minimum, map the relationship between each client and its users, agents, phone numbers, conversations, uploaded files, knowledge indexes, and integrations.
Give every client a stable, unique tenant identifier. Apply it consistently to records and requests, and derive it from the authenticated user’s permissions rather than trusting a value supplied by a browser or chatbot. A request that asks for data belonging to another tenant should be rejected, even if the requester knows that tenant’s identifier.
Isolation can be implemented in different ways, such as separate databases, schemas, or shared tables with strict tenant-aware access rules. The right design depends on the platform’s risk, scale, and operational needs. Whatever the design, document the boundary and ensure every service that reads or writes client data enforces it.
Enforce authorization at every data access
Authentication confirms who a person or service is. Authorization determines what that identity can do. A team member signed in to an agency account should not automatically have access to every client workspace, and an agent should not have permission to retrieve arbitrary files.
Use server-side checks for every sensitive action, including viewing conversations, downloading files, changing an agent’s instructions, and exporting records. Avoid relying on hidden buttons or client-side filters: those improve the interface but do not protect the underlying data.
- Assign users only to the client workspaces they need.
- Separate agency-wide administration from client-level operations.
- Restrict service accounts and integrations to specific tasks and tenants.
- Review access when staff change roles or leave the agency.
- Use multi-factor authentication for administrative accounts where available.
These controls support least privilege: each person or process receives the minimum access required to perform its job.
Keep client knowledge bases separate
Client PDFs and other reference material often power an AI agent’s answers. If files from multiple businesses are indexed together, retrieval can return an unrelated or confidential passage—even when the final answer does not cite its source. Treat the knowledge base and its search index as sensitive client data.
Maintain tenant ownership for original files, extracted text, embeddings, and indexing jobs. At retrieval time, apply the tenant filter before returning candidate content to the model. Do not depend on a prompt that says “only use this client’s files” as your security boundary; prompts guide behavior, while access controls must prevent unauthorized records from being retrieved in the first place.
Also check what happens when a file is replaced or deleted. Remove or refresh derived text and embeddings, and record which client owns each source. For highly sensitive deployments, consider separate indexes or storage resources for each tenant, balanced against the added management overhead.
Protect conversations and human handoff
WhatsApp AI agents may handle personal details, lead qualification answers, order questions, and support requests. Store each conversation with its client, agent, and channel context, and verify that the same relationship is preserved when a conversation is assigned to a human.
Handoff should not become a shortcut around isolation. An employee should see a transferred conversation only if they are authorized for that client. Notifications, email summaries, and inbox search results need the same protection as the main conversation screen. Avoid sending unnecessary personal information in notification previews.
Make the transition understandable to the customer. The agent can explain that a team member will take over, while the internal handoff note can summarize the issue using only relevant details. Clear ownership helps staff respond without copying conversations into less secure tools.
Manage models, tools, and integrations carefully
OpenAI-compatible models make it easier to choose between providers, but compatibility does not make every provider’s data practices identical. Review retention, training, processing location, and contractual terms before sending client content. Configure the application to send only the context needed for a particular response.
Apply tenant checks to tools as well as chat history. If an agent can create a CRM lead, look up an order, or call an external API, confirm that the credentials and records belong to the correct client. Prefer separate credentials per client where practical, and never place shared secrets in prompts or client-visible settings.
Maintain a list of subprocessors and integrations, including what information they receive and why. This makes reviews and client questions easier to handle.
Limit data in logs, backups, and analytics
Logs are useful for debugging, but they can quietly become a second copy of every conversation. Avoid recording full message bodies, access tokens, or uploaded document contents unless there is a defined need and appropriate protection. Redact sensitive fields and restrict log access to staff who require it.
Apply access controls and retention rules to backups, exports, and analytics datasets too. A deleted conversation may remain in a backup until its retention period ends, so make that behavior clear in internal procedures and relevant client agreements. Test that restores preserve tenant boundaries instead of combining records incorrectly.
Encryption in transit and at rest helps reduce exposure if network traffic or storage is accessed without authorization. It complements—not replaces—tenant-aware permissions, secure key management, and operational monitoring.
Test for cross-client leaks
Do not assume separation works because the interface displays different client names. Test it deliberately in development and before major releases. Create at least two test tenants with distinct users, files, conversations, and integrations, then attempt actions across the boundary.
- Try opening another tenant’s conversation by changing a record identifier.
- Ask one client’s agent questions whose answers exist only in another client’s PDF.
- Test search, exports, notifications, and human handoff—not only chat responses.
- Check background jobs, retries, and webhook events for tenant ownership.
- Confirm that unauthorized requests fail safely and produce useful audit events.
Include these checks in regression testing whenever you change authentication, retrieval, database queries, or integrations. Security reviews should cover ordinary mistakes as well as deliberate attempts to bypass controls.
A practical separation checklist
| Area | Control to verify |
|---|---|
| Identity | Users and service accounts have tenant-scoped permissions. |
| Knowledge | Files, extracted text, and retrieval results stay within the client boundary. |
| Conversations | Messages, assignments, and handoff notes retain the correct tenant context. |
| Operations | Logs, exports, backups, and integrations have controlled access and retention. |
| Assurance | Cross-tenant tests and access reviews run regularly. |
Build separation into daily agency operations
Technical controls work best when supported by repeatable processes. Use a standard onboarding checklist for each client: create the workspace, assign authorized users, connect client-specific channels, upload approved knowledge, configure tools, and test with sample data before launch. When a client leaves, revoke access, disable credentials, and follow the agreed data export and deletion process.
Record who approved access changes and who reviewed security settings. For self-hosted AI software, define responsibility for updates, database access, backups, and incident response. For managed services, ask the provider how tenant isolation is enforced and what evidence or documentation they can share.
Safe separation is a continuing practice, not a one-time setup. Agencies that treat every client workspace as a distinct security boundary can scale WhatsApp AI agents with greater confidence and give clients clearer answers about how their information is handled. Platforms such as OpenLivery can be evaluated against these same principles when comparing multi-client AI agent options.